A cluster of incidents disclosed through October 2026 raises a difficult question: how can organisations operating sophisticated digital platforms remain vulnerable to malicious releases, stolen credentials, compromised infrastructure and failures in cryptographic trust?
There is no single explanation. However, several verified reports illustrate how an initial weakness can become a wider compromise when attackers inherit permissions, manipulate trusted automation, or move between systems without encountering an effective boundary.
Code trust assurance provides a practical way to examine these relationships. It asks whether software, its dependencies, and the systems used to build, distribute, and operate it deserve the trust placed in them — and what evidence supports that judgment.
Applied properly, this approach could have reduced exposure, interrupted some documented attack paths and limited the consequences of successful intrusion. It cannot establish that every incident would have been prevented. Prevention depends on the specific weakness, the attacker’s access and whether the relevant controls remain effective under compromise.
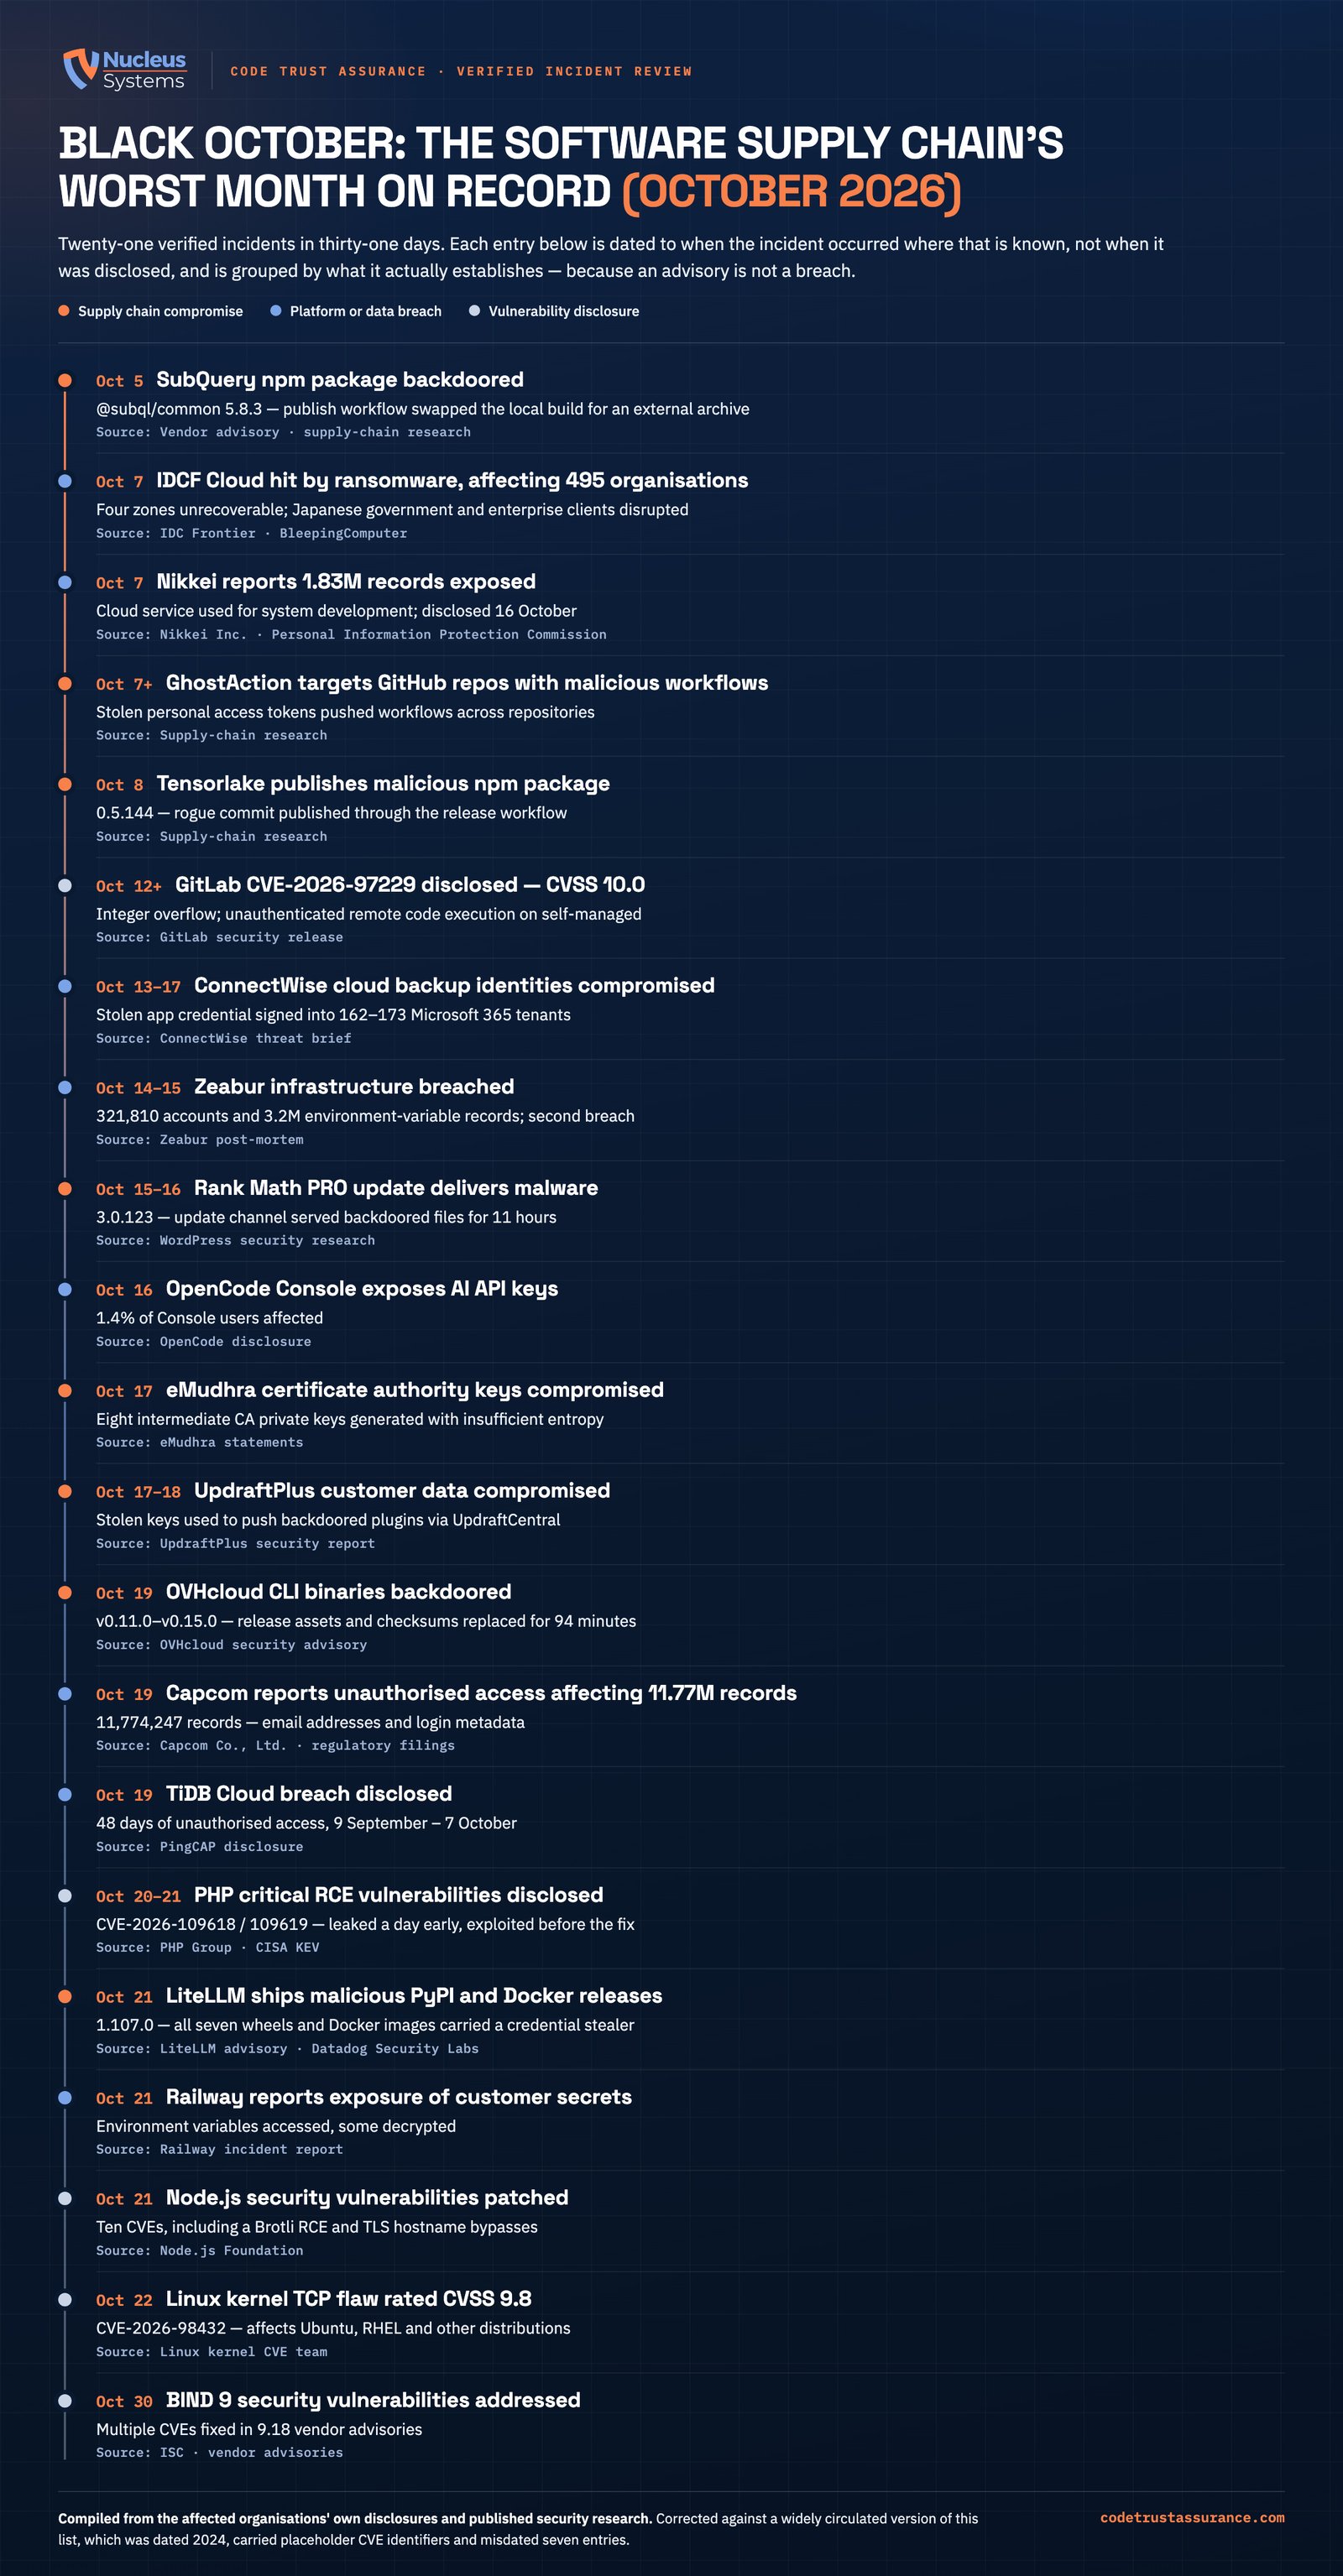
Grouped by what each incident establishes. Dates reflect when the incident occurred where known, not when it was disclosed. Compiled from the affected organisations’ own disclosures and published security research. Free to reuse with attribution.
Download JPEGFull resolution (2400×4605)Carousel (PDF, 12 pages)Establishing what the incidents actually demonstrate
October’s disclosures combine different categories of security event: reported breaches, malicious software releases, vulnerability disclosures and cryptographic failures. These should not be treated as equivalent. A vulnerability announcement does not, by itself, establish exploitation or a breach.
This analysis therefore draws on selected verified examples rather than treating a circulated list as an established incident chronology.
LiteLLM’s investigation describes a sequence involving an exposed administrative key, stolen GitHub tokens, malicious workflow activity and a release built from an attacker-controlled fork. Branch protection initially rejected a workflow change, but an organisation owner’s token was used to override it. The resulting malicious release was signed and published through the release pipeline.
Research into SubQuery’s @subql/common package describes malicious code published after changes to its CI/CD workflow. Publication used GitHub Actions OIDC through npm Trusted Publisher. This illustrates why an authenticated publishing mechanism cannot, on its own, establish that the published contents are safe.
Zeabur’s preliminary report attributes its October incident to leaked internal credentials, including long-lived administrative credentials accessible from the public internet. Railway separately reported that an attacker accessed internal systems and decrypted stored environment variables for a subset of workspaces.
Trust in an account, pipeline or platform must be constrained by controls that remain useful when that trusted component is compromised.
What code trust assurance should mean in practice
Code trust assurance is used here as an assurance discipline, rather than a claim of certification under a single universal standard. Its purpose is to connect security requirements to implemented controls, test results and accountable decisions throughout the software lifecycle.
Its scope extends beyond application source code to include:
- Third-party packages, libraries and container images.
- Build scripts, release workflows and infrastructure configuration.
- Developer identities, machine identities and publishing permissions.
- Secrets, signing keys and cryptographic operations.
- Deployment policies, runtime permissions and recovery mechanisms.
Secure development establishes practices for producing safer software. Cyber hygiene maintains the conditions those practices depend on. Technical enforcement makes critical requirements binding at the point where an action occurs. Independent validation establishes whether those restrictions work.
This is consistent with the intent of NIST’s Secure Software Development Framework: reducing vulnerabilities, limiting the impact of weaknesses that remain and addressing root causes to prevent recurrence.
The assurance question is therefore concrete: if an attacker obtains a developer account, alters a dependency or compromises a workload, which actions can they still perform — and which controls demonstrably stop them?
Secure development must protect the machinery that produces software
Application testing alone leaves an important gap if attackers can change how an application is built or published.
A release pipeline can introduce files absent from the reviewed source, retrieve an unapproved dependency or package software from an unexpected repository. Workflow definitions, build images and deployment scripts therefore require security treatment comparable to production code.
A stronger development model would require protected review of changes affecting:
- Release source repositories and permitted source references.
- Build-time scripts and dependency installation behaviour.
- Workflow permissions and access to secrets.
- Signing, publishing and production deployment.
- Infrastructure access and tenant isolation.
For sensitive changes, approval should come from someone with the expertise and authority to assess the security effect. Automated checks should also examine whether a change expands privileges, introduces a new external destination or makes an approved source configurable by an untrusted caller.
However, review requirements are only as strong as their enforcement. A control that an ordinary development identity cannot bypass may still be removable by a compromised administrator.
The architecture should therefore separate routine development authority from authority to weaken the release process. Emergency access should be narrowly scoped, time limited and independently monitored.
Malicious packages require controls beyond vulnerability scanning
A vulnerability scanner generally looks for recognised weaknesses. A newly introduced credential stealer may have no published advisory when it first appears.
Dependency assurance must consequently examine both known vulnerabilities and suspicious behaviour. Before approving a new or changed package, organisations should consider whether it introduces installation hooks, unexpected executables, obfuscated code, unusual startup behaviour or network connections unrelated to its stated purpose.
The SubQuery analysis identified credential theft and backdoor functionality associated with installation and package execution. Research into the LiteLLM compromise described malicious files capable of running during Python startup, without an application needing to import LiteLLM. These are examples of why package assessment must consider execution outside normal application functionality.
Practical enforcement could include an internal package repository that admits only approved artefacts, controlled dependency updates, exact version and integrity locking, and isolated evaluation of higher-risk releases.
Dependency installation should occur without production credentials. Installation scripts should be disabled where unnecessary, with explicit approval for packages that require them. Evaluation environments should have restricted network access and no route into sensitive infrastructure.
These controls offer different benefits. Approval gates can stop a suspicious release from entering the organisation. Isolation can reduce the consequences when detection fails. Version pinning alone is insufficient: it can faithfully preserve a malicious version once that version has been selected. Approval must establish why the selected artefact is acceptable.
CI/CD must enforce meaningful separation of privilege
A CI/CD system can combine source access, cloud access, package publishing and production deployment. That makes it a powerful target. The central design requirement is to prevent untrusted code from inheriting privileged execution.
Pull request validation should run separately from release execution. Untrusted contributions should not receive production secrets, publishing permissions or access to privileged persistent runners. Artefacts passed between stages should be treated as untrusted until verified.
GitHub’s security guidance specifically warns about privileged workflow triggers processing untrusted content. It also recommends controlling workflow dependencies and using OIDC to reduce reliance on stored, long-lived cloud credentials.
OIDC nevertheless requires restrictive trust policies. A short-lived credential can still be dangerous if any branch, repository or workflow can request it. The receiving service should verify the permitted repository, workflow, environment and source context before granting narrowly defined privileges. A test job should not be able to obtain a production publishing identity merely because it belongs to the same organisation.
These restrictions need negative testing. Assurance should demonstrate that a workflow on an unauthorised branch cannot retrieve a release credential, that a fork cannot impersonate an approved source and that a build identity cannot modify the policy governing its own approval.
Signing and provenance must be verified against expectations
Digital signatures answer questions about integrity and signing identity. They do not establish that the signer was uncompromised or that the contents are benign.
Build provenance can record how an artefact was produced. Its value depends on verifying that information against trusted expectations. SLSA’s verification guidance explicitly connects provenance to inspection and verification.
A deployment gate should therefore evaluate more than whether a signature is valid. It should establish whether:
- The artefact came from the approved source repository and reviewed revision.
- The authorised builder and workflow produced it.
- Required tests and approvals apply to that exact artefact.
- Its digest matches the artefact being deployed.
- Its signing identity and associated evidence remain trusted.
The organisation should build once and promote that same immutable artefact through environments. Rebuilding separately for production creates an opportunity for the deployed software to differ from what was assessed.
A software bill of materials supports this process by identifying components. It remains an inventory, however; it does not independently prove that those components are safe.
Cyber hygiene must make exposed credentials less useful
Credential hygiene is central to code trust because credentials determine who can change software and what software can access.
Secret detection should operate before commits are accepted, during CI and across existing repositories and artefacts. Yet detection must trigger an operational response. Removing a secret from current source does not invalidate copies already obtained. The response should include revocation, replacement, investigation of prior use and examination of related permissions.
Long-lived human tokens should be removed from automation wherever practical. Workloads should use short-lived identities with permissions limited to their specific task. Developer accounts should use phishing-resistant authentication, while session and token controls address access that survives an interactive login.
For AI services, keys should be separated by application and environment, with spending limits, rate limits and restrictions supported by the provider. A compromised development workload should not inherit unrestricted production AI access.
The important measure is the authority an exposed credential confers. A short-lived token with broad administrative permissions can still cause significant damage before it expires.
Secret storage must withstand compromise of adjacent systems
Railway’s disclosure demonstrates a distinction between encrypting stored secrets and preventing an attacker from obtaining their plaintext through compromised internal systems.
Encryption at rest remains valuable. Its protection is limited when the same compromised identity can read encrypted records and invoke the mechanism that decrypts them.
A stronger design separates storage access from decryption authority. Workloads should retrieve only the secrets they require, and bulk retrieval should require additional controls. Tenant boundaries should apply to secret access as well as to application data.
Administrative support access should be temporary and auditable. Sensitive material should be excluded from build logs, diagnostic exports and unnecessary configuration copies.
For assurance purposes, teams should test whether an ordinary platform identity can enumerate another tenant’s secrets, whether a database reader can invoke decryption and whether unusual retrieval volume produces an actionable response. These tests turn a general claim about encryption into evidence about actual access boundaries.
Runtime restrictions can contain software that passes earlier checks
Even a carefully controlled build process will sometimes admit vulnerable or malicious software. Runtime controls provide another opportunity to interrupt harm.
Applications should operate with the minimum filesystem, network and cloud permissions needed for their function. Containers should avoid unnecessary root privileges and privileged host access. Sensitive credentials should not be available to unrelated processes.
Network egress restrictions are especially relevant to credential theft. A malicious package may execute successfully yet fail to send collected information to an unauthorised destination.
Such restrictions need careful design. Broad outbound HTTPS access can permit exfiltration, while an overly restrictive policy can disrupt essential services. The objective is to identify legitimate communication requirements and enforce them through controlled paths. These measures primarily contain impact. They should not be presented as proof that malicious code cannot execute.
Cryptographic assurance must test generated outputs
The eMudhra incident illustrates why assurance must extend to the outputs of security processes.
Its statements acknowledge recoverable private keys associated with eight intermediate TLS certificate authorities and attribute the weakness to a script error. The company also states that HSMs were used during key generation. The lesson is that approved equipment does not, by itself, validate every operation or resulting key.
Cryptographic assurance should examine the complete generation, import, wrapping, export and publication process. It should include independent review of ceremony tooling, strict control of parameter changes and checks designed to identify known weak-key conditions.
Some defects can be detected from public keys. Broader confidence in randomness and key generation requires evidence about the underlying process and implementation; no single public-key test proves adequate entropy.
Technical enforcement should prevent publication when mandatory checks fail or required evidence is missing. This moves validation to the point before a weak output becomes part of a wider trust infrastructure.
Vulnerability management and ransomware resilience remain essential
Code trust assurance must also address conventional vulnerabilities and operational compromise.
For disclosed weaknesses, organisations need an accurate inventory linking software versions to deployed workloads and accountable owners. Remediation priority should reflect exposure, exploitability, privileges and service importance.
Where immediate patching is impractical, temporary controls may include disabling affected functionality, restricting network access or isolating a workload. Closure should require verification of the deployed fix.
For ransomware, development controls help where the entry path involves vulnerable software or compromised updates. Wider resilience also requires protected administrative identities, segmentation, endpoint controls and backups isolated from routine production authority.
Recovery testing must demonstrate that essential services can be restored within required times, that backup deletion is restricted and that recovered environments do not simply reintroduce compromised credentials. A successful restore can reduce disruption. It cannot reverse data already stolen.
Validation must demonstrate refusal as well as success
The most valuable assurance tests often attempt actions that should be impossible.
Can a developer deploy an unsigned artefact? Can a build job request another environment’s secrets? Can one compromised identity both weaken a release rule and approve the resulting release? Can an administrator erase the only evidence of an override?
Testing should use controlled environments, synthetic secrets and agreed boundaries. It should cover configuration changes and policy drift as well as the initial implementation.
Evidence should include the attempted action, the expected restriction, the observed result and any corrective work. Logs should be retained outside the administrative boundary of the system being assessed.
Independence matters because the people operating a control may share assumptions about how it works. A reviewer should be able to reproduce material results and challenge exceptions. Automation can collect evidence continuously. Human judgment remains necessary to assess whether the policy itself is adequate and whether exceptions create unacceptable exposure.
Making code trust assurance operational
Organisations can begin by identifying their most consequential trust transitions: source to build, build to registry, registry to production, workload to secret store and administrator to security policy.
For each transition, they should define the permitted action, identity, evidence and enforcement mechanism. They should then test whether an attacker controlling one side can bypass the restriction.
Useful measures include the proportion of production deployments subject to enforced verification, the number of persistent privileged credentials, time to revoke an exposed secret, coverage of tenant-isolation tests and success rates for restoration exercises.
Exceptions require owners, expiry dates and compensating controls. A permanent bypass gradually becomes part of the normal operating model.
The incidents examined here show why the security of a trusted system must include what happens when its trust is abused. Secure development reduces the introduction of weaknesses. Cyber hygiene reduces exploitable exposure. Technical enforcement restricts what a compromised identity or component can do. Independent validation establishes whether those restrictions hold.
Together, these practices could have blocked particular steps in the documented attack chains and reduced the reach of others. The defensible promise is measurable reduction in exposure and impact, supported by evidence about the controls that protect each critical boundary.
Where the framework formalises this
Every control discussed above corresponds to a scored requirement in the Nucleus Systems Code Trust Assurance Framework (NS-CTAF). The framework turns these judgments into evidence and a number.
Developer and machine identity, signing, attribution.
Artefact integrity, provenance verification, tamper evidence.
Pipeline protection, review enforcement, privilege separation.
Package approval, isolation, integrity locking.
Least privilege, egress control, drift detection.
Exceptions, ownership, independent validation.
Incident descriptions in this article are drawn from the affected organisations’ own disclosures and published security research. They are summarised to illustrate control design, not to characterise any organisation’s overall security posture.